Davoud Teimouri

Davoud Teimouri

Professional blogger, vExpert 2015/2016/2017/2018/2019/2020/2021/2022/2023/2024/2025, vExpert NSX, vExpert PRO, vExpert Security, vExpert EUC, VCA, MCITP. This blog is started with simple posts and now, it has large following readers.

How to Export Big Virtual Machine (>2TB) as OVA or OVF
I guess, you know the instruction but let's quick review. You can export virtual machines via some different tools such as vSphere Client, vSphere Web Client and others. All administrators do it today and familiar with OVA and OVF. It's possible to export small virtual machines via vSphere Client, vSphere Web Client, PowerCLI. If you want to export virtual machine with 200~300 GB virtual disks (Thin or Thick), there is serious problem, just make sure that you have enough free space. But did you try to export big or monster VM as OVA or OVF?
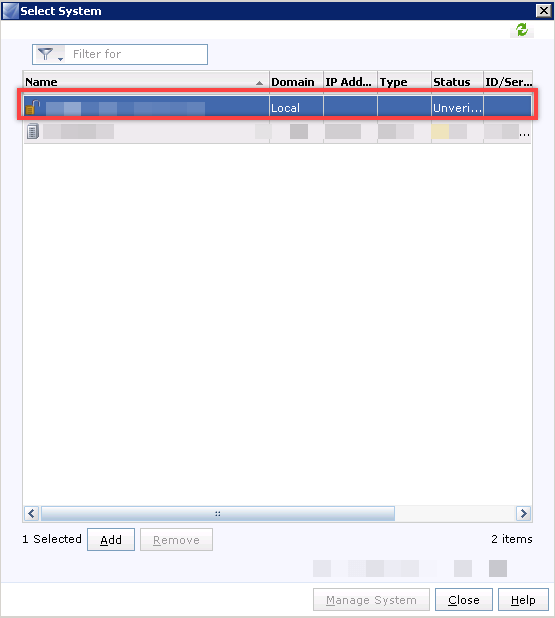
VNX 2 Series: Best Solution to Remove Unverified Systems

VNX Domain - Unverified Systems

VNX Storage arrays can be added to a domain for centralization logging and management for multiple storage arrays. Also Unisphere Central can be added to a VNX domain.

Sometimes, storage administrator makes mistake about adding or removing VNX storage arrays from VNX domain. As an example, administrator has to remove a VNX for send to repairing but forget removing storage array from domain. Another example, when there is multiple domains with multiple range of IP addresses, may be administrator add array to domain wrongly and after that, change IP and add to another domain.

In these situations, domains will contain some systems as unverified system, the unverified systems should verify again and otherwise should be removed.

Virtual Environments Vulnerability Assessment By GSM (OpenVAS) – Part 3

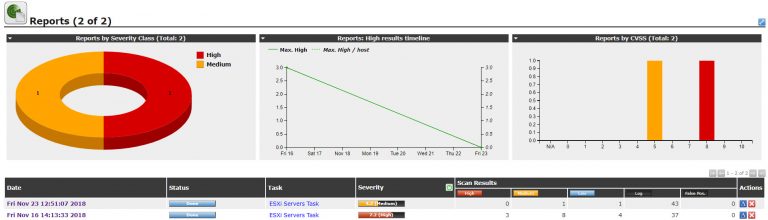
GSM Community Edition - Report Comparison

At the first part, we've reviewed GSM (Greenbone Security Manager - Formerly OpenVAS) as a security manager or assessment tool for discovering vulnerabilities on virtual environments, the second part was more functional and we talked more about GSM. You leaned that how can you create a target on Greenboone Security Manager and scan it to discover vulnerabilities.

As I said at the end of second part of the blog post, the third part is related to resolving security issues. Any software and specially operating systems have "Hardening Guide". You must follow steps of hardening guide to reduce security vulnerabilities effect on production environments.

Virtual Environments Vulnerability Assessment By GSM (OpenVAS) – Part 2

Virtual Environments Vulnerability Assessment By GSM (OpenVAS) - Part 2

We have reviewed reasons of have Vulnerability Assessment or Vulnerability Manager in virtual environments and how these software help us to find vulnerabilities on any component of virtual infrastructure. We have reviewed OpenVAS or Greenbone Security Manager and talked about features and abilities.

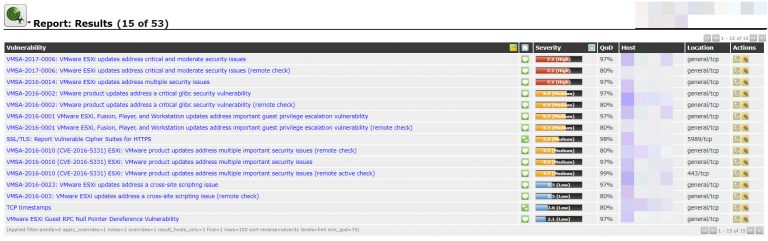
Now, it's time to use the GSM server that we had prepared on the previous part. In this part of blog post, we'll configure a target (ESXi Server) on OpenVAS server, create a task for scan and find the result of scan.

I've installed ESXi 6U1 (3029758) on a virtual machine and there is no customized configuration, all configurations are default.

NFTables, The Next Generation of Packet Classification Framework

iptables vs nftables

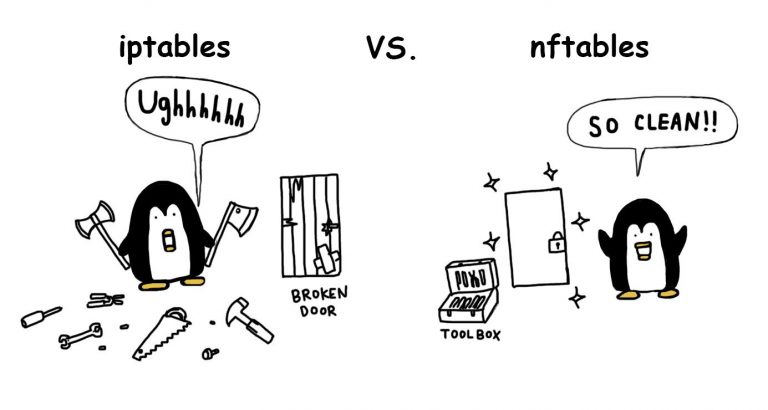
Over the years, XTables (IPTables, IP6Tables, ARPTables and EBTables) were using as user-space utility programs for packet filtering in Linux distributions such as Red Hat Enterprise Linux or Ubuntu. Now, Linux vendors are replacing XTables with next generation packet classification framework which called NFTables.

nftables replaces the popular {ip,ip6,arp,eb}tables. This software provides a new in-kernel packet classification framework that is based on a network-specific Virtual Machine (VM) and a new nft user-space command line tool. nftables reuses the existing Netfilter subsystems such as the existing hook infrastructure, the connection tracking system, NAT, user-space queuing and logging subsystem.

Virtual Environments Vulnerability Assessment By GSM (OpenVAS) – Part 1

Vulnerability Assessment

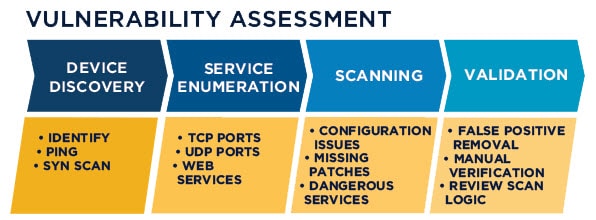
In virtual environments, any vulnerability has affect on virtual infrastructure and those who get the service including internal and external services. So at least, any organization should have process to identifying vulnerabilities. Identifying vulnerabilities needs tools in IT infrastructure to scan devices, operating systems and applications and find vulnerabilities (Especially security vulnerabilities).